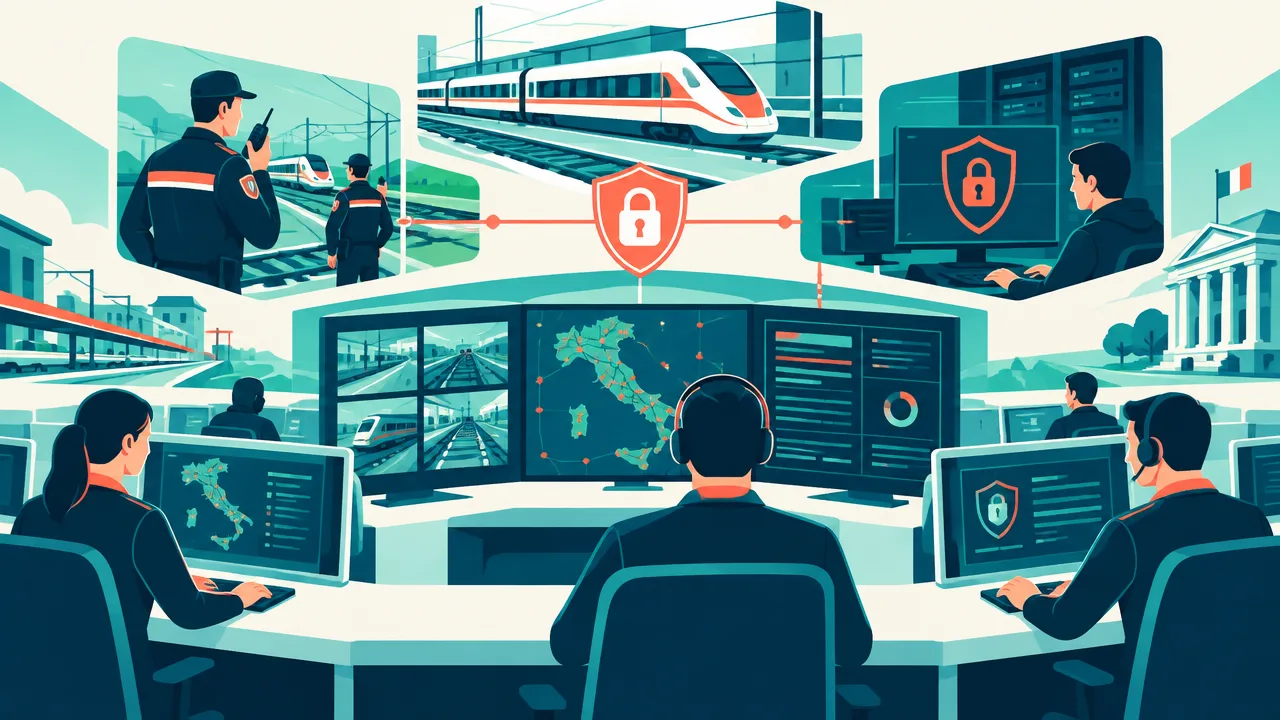
Ferrovie dello Stato raises security levels and strengthens protection of physical and digital infrastructures. The group led by Gianpiero Strisciuglio has activated the device planned for complex situations, deploying a system combining over 1,300 operators on the ground, a central operations room functioning twenty-four hours a day, and a structure specialised in cyber defence.
against cyber attacks
The objective is to protect travellers, employees and facilities, preventing network threats from causing interruptions or repercussions on the regularity of connections. It should be noted that the strengthening of measures is part of a national framework focusing on the protection of essential services.
against cyber attacks
At Palazzo Chigi, work is underway on new protocols and a control room to coordinate the government's response. For the railway sector, the key point is to combine two dimensions of security: maintaining surveillance of spaces and infrastructures and protecting the digital systems that support the group’s operations.
against cyber attacks
Not two separate fronts, therefore, but components of a single prevention and response organisation.
Coordination is entrusted to the Security Directorate, which brings together activities protecting people, travellers, personnel and infrastructures with those of cybersecurity. This is an integrated surveillance model: information gathered on the ground and reports from the various companies must contribute to the assessment of risk situations.
The device therefore does not end with the presence of staff, but includes monitoring, anomaly detection and connection between operational structures.
The field component includes over 1,300 operators distributed nationwide, supported by technological monitoring and prevention tools. This figure refers to the overall surveillance deployed by the group: it is not a team of 1,300 specialists against hacker attacks.
Cyber defence is entrusted to a dedicated structure, while the operators make up the territorial component of the protection system. This distinction is important to understand how Ferrovie’s response to different types of threats is structured. At the heart of the organisation is the Central Operations Room, active every day, without interruption.
The structure monitors evolving risks, identifies any anomalies and maintains the link with the operational rooms of the group’s companies. The connection with the Railway Police and other law enforcement agencies completes the device, enabling coordination between company surveillance and the competent authorities.
Specialist technological systems support the recognition of critical situations and the collection of the information needed to manage them.
On the digital front, the protection perimeter includes networks, infrastructures, applications and information systems. The cybersecurity structure also handles the management of cyber incidents for all the group's companies: its role, therefore, involves not only prevention but also response when a problem is detected.
The declared aim is to prevent a digital threat from compromising the operation of the network and continuity of rail services, integrating technological defence with other security activities. The Security Directorate manages collaboration with competent security and defence bodies, while the operations room maintains the necessary links to manage critical situations.
The announced strengthening therefore concerns the entire protection chain: from presence on the ground to technological surveillance, from assessment of reports to incident management.
Umberto Mancini
Sources and documents
Original article by Umberto Mancini.